Our team’s vulnerability disclosures 2021

September 22, 2022

At Faraday, we are part of the open-source community. Our product relies on various open-source projects, and it is released under the GNU General Public License. Fortunately, these practices are becoming more common and, with them, open-source software is increasing its presence in data centers, consumer devices, and applications.

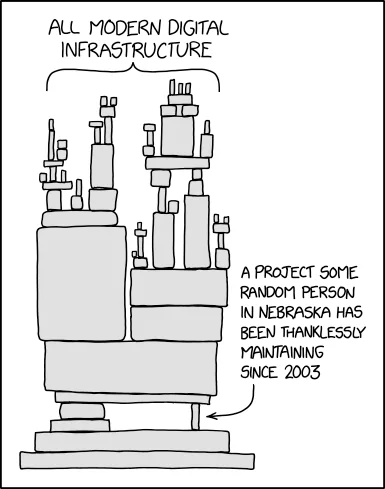
But this can have its drawbacks, too, as this xkcd comic illustrates. In particular, some of the software we use daily does not have security in mind. In many cases, these tools started as small side projects or weekend experiments, and their creators did not foresee the popularity they might achieve in the future. Regardless of why this happens, and after reflecting on this, our research team started a new quest to find and report vulnerabilities in the open-source projects we use every day.

These are the vulnerabilities we’ve disclosed during 2021

– CVE-2021–4021: Uncontrolled resource consumption via specially crafted ELF64 binary for MIPS architecture in radare2.

– CVE-2021–4022: Segfault when analyzing an ELF64 for HPPA architecture in rizin.

– CVE-2021–43814: Heap-based OOB write when parsing dwarf DIE info in Rizin.

– CVE-2021–4166: Out-of-bounds Read while loading session in vim.

– CVE-2021–4192: Use After Free while loading session in vim.

– CVE-2021–4193: Out-of-bounds Read while loading session in vim.
Continue Reading

The latest handpicked blog articles

As security programs grow, more people need to create and manage their own work, and more time goes into everyday navigation. Faraday 5.24 tackles both. It brings a new role

October 20, 2026

This year, we were once again part of Ekoparty with our own booth, where we welcomed clients, colleagues, and cybersecurity professionals, showcased FaradAI in action, challenged the community with our

October 14, 2026

Anyone can find a bug in a deliberately-vulnerable app. The harder question — the one that actually matters in production — is: can you run a real security program end to

September 30, 2026

Stay Informed, Subscribe to Our Newsletter

Enter your email and never miss timely alerts and security guidance from the experts at Faraday.

Faraday provides a smarter way for Large Enterprises, MSSPs, and Application Security Teams to get more from their existing security ecosystem.

Headquarters

Research Lab & Dev

Solutions

Open Source

© 2025 Faraday Security. All rights reserved.
Terms and Conditions | Privacy Policy
#zsiq_float, .zsiq_floatmain, [id^="zsiq"], [class^="zsiq"], iframe[id*="salesiq"], iframe[title*="chat" i] { display: none !important; visibility: hidden !important; opacity: 0 !important; pointer-events: none !important; }