Not every workspace carries the same risk. A critical finding in a staging environment doesn’t weigh the same as one in a production system that runs your business, yet most platforms score them with a single, fixed formula.
Faraday 5.25 puts prioritization back in your hands. This release also brings your security stack together with 176 new integrations, lets reports deliver themselves, and gives pentesters a faster way to capture findings. Here’s what’s new.
Highlights
- Risk Score Profiles: prioritize risk your way
- 176 new Runners: your entire security stack, in one place
- Capture to Faraday: log findings without leaving the browser
- Report Subscriptions: the right report, to the right people, on schedule
- More reliable data and stronger access control
- Additional improvements
Prioritize Risk Your Way with Risk Score Profiles
Security teams that manage multiple clients, business units or environments know that one formula doesn’t fit all. Until now, every workspace was scored the same way.
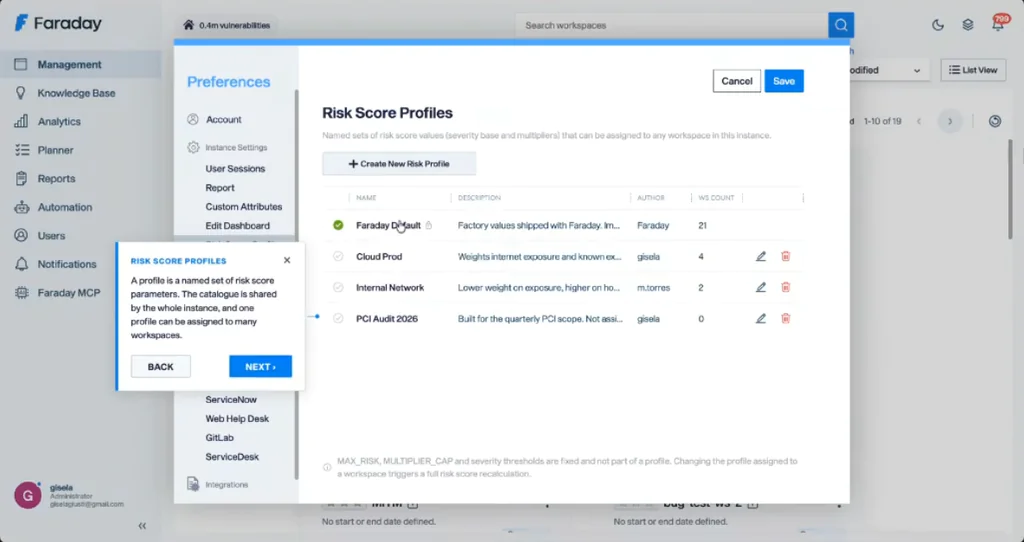
With Risk Score Profiles, administrators and Workspace Administrators can create named, reusable profiles from Preferences > Faraday Instance > Risk Score Profiles:
- Define the base value for each severity level
- Set the multipliers that raise a vulnerability’s score
- Assign a profile to each workspace based on its own risk priorities
- Set a personal default profile that applies to every new workspace you create
When you change a workspace’s profile, its risk scores are recalculated in the background. Faraday’s built-in default profile is always available as a protected baseline.
Why it matters: your team focuses first on what’s truly critical for each part of the business, and leadership sees risk measured by criteria that make sense to them.
Your Entire Security Stack, in One Place: + 300 Runners and counting
Security data lives across dozens of tools, and consolidating it is often a manual job. The Faraday Runners catalog now covers cloud security, code scanning (SAST/SCA), EDR/XDR, attack surface management, threat intelligence, identity, SIEM, DAST and bug bounty platforms. That includes Wiz, Prisma Cloud, Checkmarx, Veracode, CrowdStrike, SentinelOne, Splunk, Okta, Censys and HackerOne.
Highlights:
- Code scanners can clone the repository to scan, including private GitHub and GitLab repos
- AI pentesting integrations for Strix, XBOW, Aikido and AWS Security Agent
- Compliance integrations for Vanta, Drata and Sprinto, with failing controls imported as vulnerabilities
- Vicarius vRx integration for assets, vulnerabilities, patches, software and incidents
- A bundled set of open-source scanners in the Docker image, plus a script to generate Kubernetes deployments for the dispatcher
Why it matters: fewer blind spots and less manual work. Every finding, from code to cloud to compliance, ends up in a single place where you can prioritize it.
Log Findings Without Leaving the Browser: Capture to Faraday
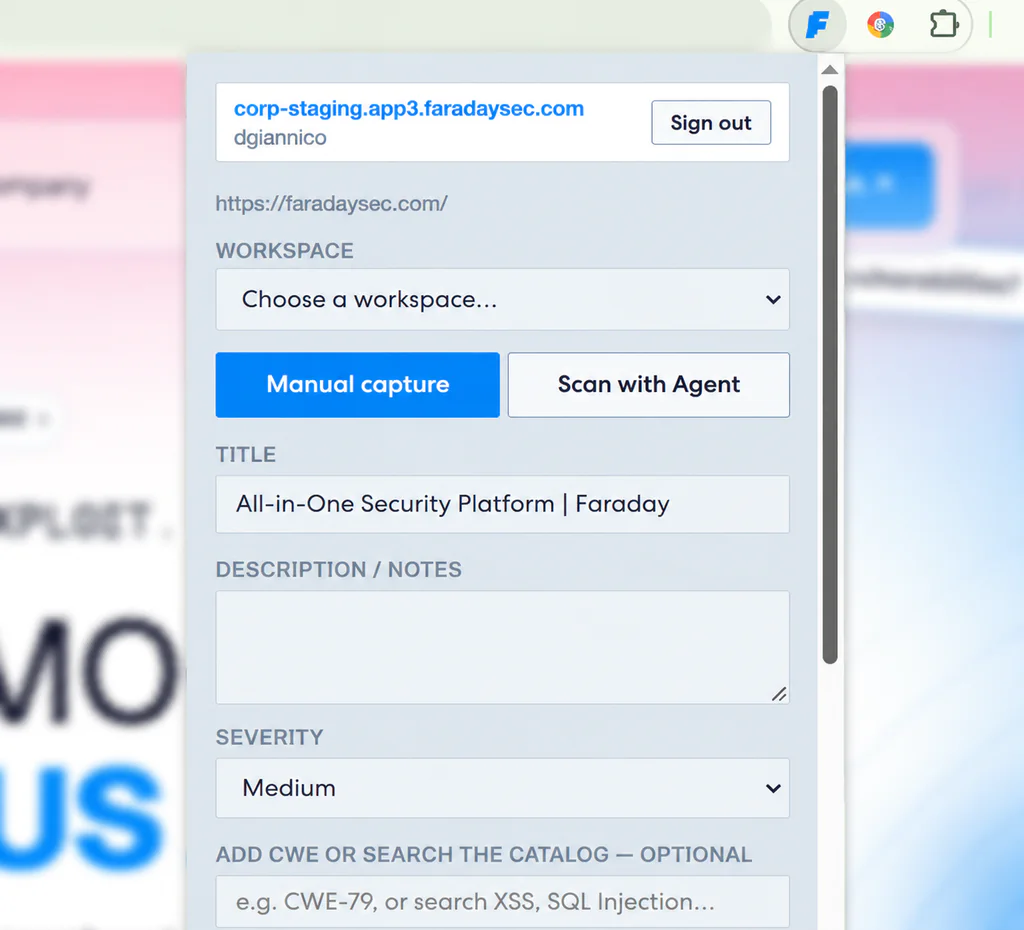
During manual testing, switching tools to document a finding breaks the flow. Capture to Faraday is a new Chrome extension that lets you log a finding directly from the page you’re testing, with a screenshot attached automatically. You can also run any online Runner against the current target from the same popup. Your data goes straight to your Faraday instance.
Why it matters: pentesters spend less time documenting and more time testing.
The Right Report, to the Right People: Report Subscriptions
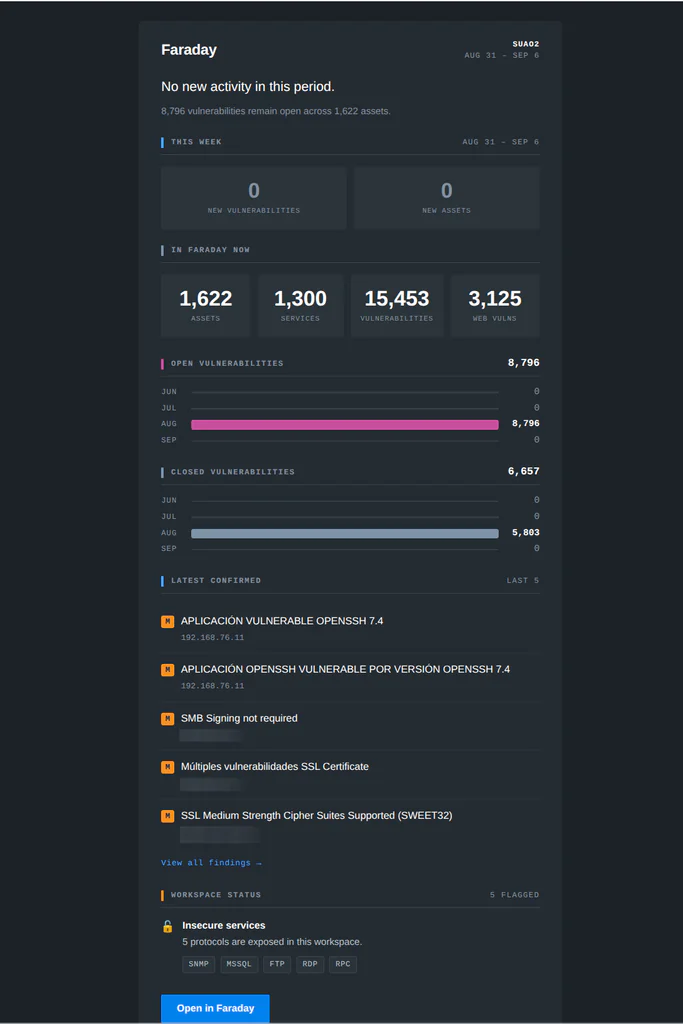
Weekly Reports is now Report Subscriptions, and it is far more flexible. Instead of a fixed list of workspaces with an on/off toggle, you create subscriptions in Reports > Report Subscriptions. Each one combines:
- A workspace
- A schedule: weekly, biweekly or monthly
- The sections you want included
- The delivery method: email to a list of recipients, saved in Faraday for later download, or both
Why it matters: each stakeholder gets the information they need, when they need it, and nobody has to remember to send it
More Reliable Data and Stronger Access Control
Some of the most important work in this release isn’t visible on screen, but it shapes how much you can trust what you see:
- No more silently dropped findings: Nessus imports now keep the severity shown in the report, even when a vulnerability has no CVSSv3 score
- Clear import summaries: each report import sends a single notification showing what was created, updated or unchanged, plus anything that couldn’t be imported
- Accurate timelines: re-imported open or re-opened vulnerabilities now refresh their Last Detected and update dates
- Access token validation improvements
Additional Improvements
- Richer dashboards: new Tools Activity, Security Scanners and Credentials widgets, a redesigned workspace risk score widget, and an Activity Feed that reads as a timeline
- Quicker search: type a plain string and Faraday searches the primary field automatically
- Services table: search by Description and number of Vulnerabilities, plus new Description and Owned columns
- New import plugin: Google Security Command Center (CSV)
For the full list of fixes, see the changelog.
Looking Ahead
Faraday 5.25 is about putting control in your hands: how you score risk, where your data comes from, and who gets informed. As always, we’d love your feedback. Reach out to our support team and tell us what you’d like to see next.
See you in the next release!