Focus on what Matters
Optimizing your security posture by drastically reducing the time spent on executing, managing, and prioritizing.
We keep delivering enhancements to our users to ease vulnerability management and pentesting procedures. In this new version, you will have a risk scoring with easy-to-grasp representation; It is not just an objective framework for evaluating a security posture but a curated selection of filters to prioritize according to a determined context.Scale Application Security Successfully and distill thousands of vulnerabilities to the handful that are exploitable and require attention.
Prioritizing is a time-saving priority; now you will be able to filter vulnerabilities as a hacker would.
Reduce the noise and focus on what’s actually exploitable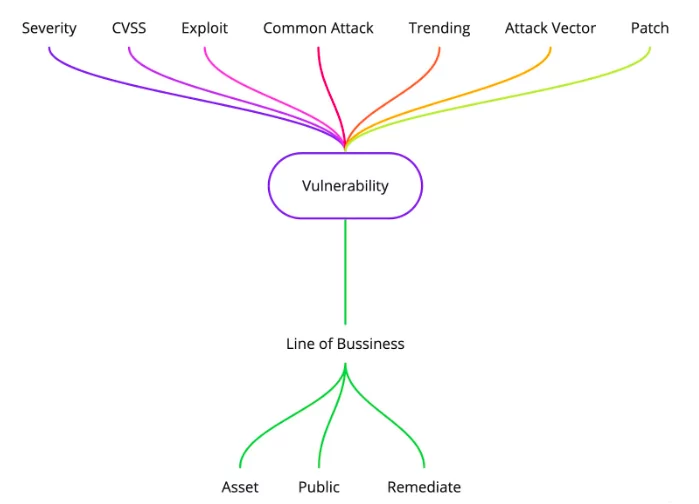
Deliver multiple reports with templates
New Report templates allow teams to improve their executive summaries. Reduce reporting time and keep your team focused on your findings.
Our platform supports Jinja2 syntax, so you can create your reports in a personalized way without much effort.
Use our own templates or create your own!
Other Improvements
Feedback is gold, you requested we listened. This last item belonged to our previous version and was brought about with new details. We have incorporated into our v4 version our “command history” but with some restyling. Now, by simply clicking on the icon on the right you copy the whole command.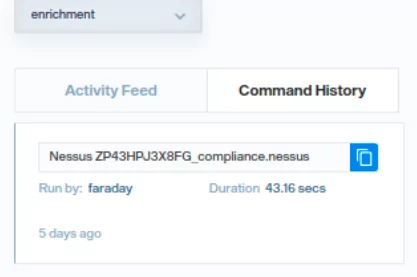
New features:
Command history added to dashboard
New Enrichment feature (Corporate)
Risk Score calculation (Corporate)
New report template Pci / Wmapps / Web apps (Professional / Corporate)
Add CVE / Risk Score / CVSS2 / CVSS3 filter to searchbar
Add importants to Asset and Workspace
Update vulns with Faraday-Cli

Product update:
Update reports view
Update assing tags modal
New Plugins for Invicti / Nessus-SC
Improve Grype plugin
Add Qualys agent executor

Bug fixing:
Fix in Markdown grouped template
Add custom attributes in KB
Fix security issue in Agents view
Fix Asset Owner permission
Fix Duplicates feature
Fix Edit scheduler view
Want to know more? Book a call